HIPAA-compliant meeting bot API for healthcare software
MeetStream is HIPAA compliant and signs Business Associate Agreements, so healthcare software can record clinical calls, provider training and research interviews. Every recording lands in storage you own, encrypted in transit and at rest.
What healthcare teams need from a meeting bot API
Capture you can defend starts with scope, then with where each recording goes and who can reach it.
Recordings stay in your own S3 bucket, in your own account.
In transit and at rest, on every recording and transcript.
Complete on Zoom, and speaker-attributed on Meet and Teams.
The bot reads the schedule through the Calendar API.
The security page lists every control.
From a meeting link to your product
One request puts a bot in the call. A webhook tells you when the files are ready.
- A named bot in the roomPeople can see it, which helps with disclosure and consent.
- Records and streams liveAudio and video while the meeting runs, on all three platforms.
- Events as they happenParticipant events carry the timeline of who joined and when.
What you get from every recording
The meeting bot API overview covers all three platforms.
Your data stays in your account
Recordings and transcripts go straight to a bucket you own, in the region you pick.
- Your retention, your accessYou set the rules on your own bucket, and sensitive content rests inside your boundary.
- Thirty days otherwiseFiles stay in MeetStream storage for thirty days.
- Regions you chooseThe United States by default, with the EU, Australia, Japan and the Middle East open.
Reliable speaker attribution on every recording
A clinician and a patient are named by the platform itself, and so are a trainer and a trainee or a researcher and a study participant.
| Platform | What the bot returns |
|---|---|
| Zoom | Complete, one isolated audio stream per participant |
| Google Meet | Speaker-attributed audio, named by the platform |
| Microsoft Teams | Speaker-attributed audio, named by the platform |
Names come from the call, not from a model. Speaker diarization covers the difference.
Where MeetStream stands on healthcare compliance
MeetStream is HIPAA compliant and signs Business Associate Agreements. It is ISO 27001 certified, and SOC 2 Type 2 is under audit.
- A BAA before PHI flowsSign a Business Associate Agreement with MeetStream before protected health information reaches a bot. HIPAA is shared: we cover our part under the BAA, and your application keeps its own access controls and audit trail.
- Your security boundaryBring your own S3 bucket and every file lands inside it, under your retention rules.
- Your choice of transcriptionDeepgram, AssemblyAI, Sarvam, JigsawStack or native captions, so the provider fits your own vendor review.
Healthcare workflows that run today
With a BAA in place, clinical calls run alongside everything else.
| Call type | What runs today |
|---|---|
| Telehealth visits and care coordination | Under a signed BAA, with retention and storage you control |
| Internal training and case teaching | Per-participant audio and any transcript engine |
| Research interviews | People consent first, and files land in your own bucket |
| Vendor and operations meetings | Joined on schedule through the Calendar API |
| Product feedback with clinicians | About software rather than patients |
Care coordination touches a patient record, so put the BAA in place before those calls run. The compliance recording page covers retention.
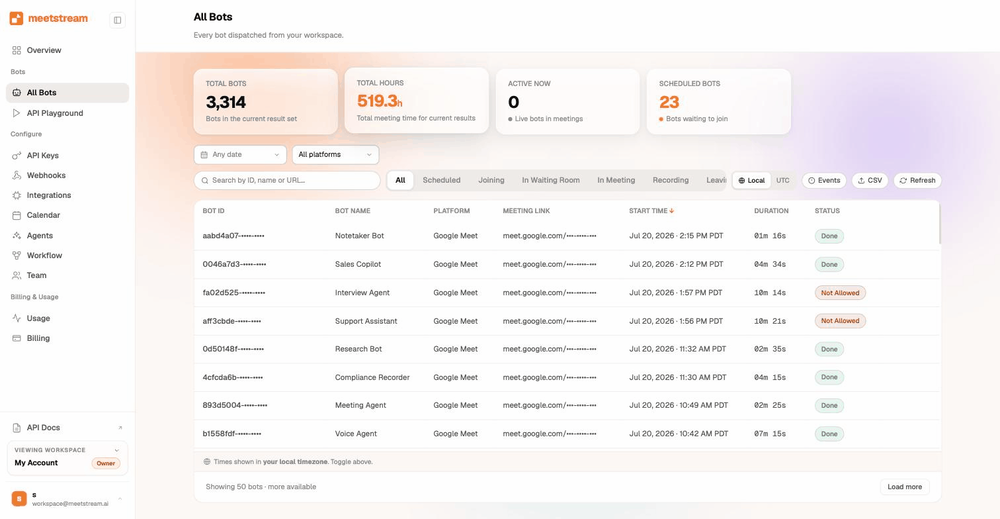
Enterprise-level security, keep your data private.
The certificate, the audit status and the Trust Center are all on the security page.
MeetStream is ISO 27001 certified and HIPAA compliant, with BAAs available. SOC 2 Type 2 is under audit rather than complete.
MeetStream is GDPR compliant, and bots run in the United States by default.
Bring your own S3 bucket and recordings land there from the first byte.


Healthcare bot limits and defaults
Email info@meetstream.ai to scope the agreements your build needs.
Got a question? We got the answer.
Common questions about healthcare capture. What fits, where files live, and how speakers are named.
Where are recordings stored?
In MeetStream storage, 30 days are included at no charge, and you can adjust that per bot. Or use your own S3 bucket, where nothing is written to ours.
Does MeetStream handle protected health information?
Yes, under a signed Business Associate Agreement. MeetStream is HIPAA compliant; ask for a BAA before PHI reaches a bot, and keep access controls and audit logging for your own users in your application.
Can we separate clinician and patient audio?
Yes. Per-participant audio is complete on Zoom and speaker-attributed on Google Meet and Teams. A clinician and patient call carries PHI, so put the BAA in place first.
Does MeetStream sign a BAA or offer HIPAA compliance?
Yes to both. MeetStream is HIPAA compliant and signs BAAs. It is also ISO 27001 certified, and SOC 2 Type 2 is under audit. HHS issues no official HIPAA certification, so no vendor can honestly claim one.
Can recordings stay inside our own infrastructure?
Yes. With bring-your-own S3, recordings and transcripts go straight into your bucket. They sit inside your own security boundary. Your own retention rules apply.
Capture that stays inside your own account.
Provider training, research interviews and vendor calls, recorded through one API and written to storage you own.
Build it in an afternoon
One API to join, record, stream, and transcribe meetings across Zoom, Google Meet, and Microsoft Teams.